Skip to content
Beta

Rehost to STACKIT: Spring Boot and PostgreSQL Overview

Last updated on

Stackit LogoStackit Logo
STACKIT

Rehost to STACKIT: Spring Boot and PostgreSQL Overview

Plan a Spring Boot and PostgreSQL Rehost to STACKIT: discovery, VM design, landing-zone readiness, migration decisions, operating handoff, and optimization.

PLAN

Spring Boot Rehost Journey

Open with the complete Migration Framework so the audience can place workload assessment, Rehost design, controlled migration, stabilization, and optimization in one end-to-end journey.

STACKIT Cloud Migration Framework Journey across the four phases Assess, Design and Mobilize, Migrate, and Run with their key modules. Assess PHASE 1 Assess Design & mobilize PHASE 2 Design & mobilize Migrate PHASE 3 Migrate Run PHASE 4 Run PLANNING Discovery Discovery Map apps and dependencies. Design Design Define target patterns. Migration plan Migration plan Sequence waves for delivery. Rapid discovery Rapid discovery Inventory workloads to create an early scope and cost baseline. TCO report TCO report Model migration economics to support investment and planning decisions. Readiness assessment Readiness assessment Assess technology and organization gaps before detailed design starts. Deepdive workshop Deepdive workshop Explore STACKIT services and platform options for target design. Briefings & workshops Briefings & workshops Align stakeholders on goals, scope, and migration expectations. Business case Business case Compare value, effort, and investment per application. Enablement ENABLEMENT Center of Excellence Trainings & Learning Paths Documentation & Reference Landing zone Landing zone Establish the secure platform base for migrated workloads. Security & compliance Security & compliance Define security and compliance controls for migration and operations. Target operating model Target operating model Define roles, processes, and ownership for target operations. Migration factory setup Migration factory setup Prepare teams, tools, and runbooks for scalable migration execution. Migrate MIGRATE Relocate Relocate Rehost Rehost Replatform Replatform Optimize Optimize Improve sizing, performance, and cost after cutover. Repurchase Repurchase Evaluate SaaS options when replacement delivers better value. Refactor Refactor Restructure strategic workloads for cloud- native scalability and agility. Operating model handover Operating model handover TOM validation and ownership transfer Hypercare Hypercare Post-cutover stabilization bridge. Operate Operate Steady-state cloud operations. Support Support Manage incidents and service requests across support responsibilities. Customer Success Customer Success Track adoption, outcomes, and value realization with stakeholders.
STACKIT Migration Framework from Assess through Design and Mobilize and Migrate to Run
PLAN

Rapid Discovery

Build a lightweight workload baseline for the Spring Boot runtime, PostgreSQL data path, dependencies, and initial capacity signals. Use it to qualify migration intent, expose unknowns, and define what detailed Discovery must validate before target design; do not treat early assumptions as verified inputs.

AssessRapid discoveryOverview In 4 trails
Rapid discovery process Input data is processed through rapid discovery tooling to produce decision-ready outputs for early migration choices. Input dataCMDB & inventory exportsAsset lists, hosts, base platform factsHypervisor & cloud reportsUsage, footprint, and utilization signalsPlatform listsKubernetes, database, and OS baselinesRapid discovery toolingIngest & normalize datasetsStandardize source records and schemaClassify & aggregate assetsConsolidate by technology and quantityApply assumptionsConfidence levels and growth factorsOutput informationConsolidated asset baselineFact base for scope and planningInitial STACKIT sizingFirst capacity assumptionsPrice indication & TCO corridorEarly cost orientation for decisions
Rapid Discovery process from source data collection to a decision-ready migration baseline

Rapid Discovery provides a fast, automated baseline of the current environment across on-premises and cloud landscapes. The focus is on quantifying the existing IT portfolio in a short time window, so teams can make early migration and commercial decisions with confidence.

At this stage, quantity and distribution matter more than deep application relationships.

STEP

Discovery

Combine application-owner evidence with technical measurements of dependencies, Java and PostgreSQL versions, service behavior, data size and change rate, operating constraints, recovery objectives, and representative resource use. Confirm compatibility, migration constraints, and the target capacity baseline before design.

Design and mobilizeDiscoveryOverview In 4 trails
Discovery source-to-decision flow Discovery separates technical and human-driven inputs, runs technical-first and human-enriched analyses, and hands over both insight streams to follow-on modules. Discovery inputsTechnical and automated discoveryInfrastructure inventoryCMDB, VM, database, middleware, storageRuntime and utilization dataCPU, memory, I/O, network and seasonalityIntegration and flow signalsNetwork paths, APIs, identity, data movementAssessment-driven human inputSecurity and compliance contextData classes, controls, audit requirementsOwner and business inputCriticality, release windows, lifecycle plansDiscovery analysis toolingTechnical-first analysesNormalize and correlateUnify records and technical identitiesDependency mappingInfer communication and couplingUtilization and sizing analysisEstimate baseline demand corridorsPreliminary segmentationCluster by stack and environmentHuman-driven analyses (application owner input)Criticality and risk calibrationValidate business impact and constraintsWave feasibility and sequencingReconcile dependencies with release windowsAssumption and gap registerTrack open points and confidenceHandover outputsTool-derived outputsDesignTarget architecture options and sizing factsLanding zonePlatform guardrails and account structure needsMigration planWave backlog, sequencing, and cutover windowsAssessment-validated outputsSecurity and complianceControl needs, data classes, remediation pointsOperating modelRole model, ownership boundaries, process impactBusiness caseValue/risk profile and modernization priorities
Discovery analysis combining technical and application-owner evidence

Discovery is one of the first and most critical modules in the Design and Mobilize phase. It refines Rapid Discovery results and adds the depth needed to make architecture and migration-wave decisions with confidence.

The primary objective is to establish a realistic, evidence-based understanding of the current IT landscape, business priorities, and organizational readiness before detailed target design and migration planning are finalized.

LIFT

Rehost Strategy

Use Discovery evidence to confirm that preserving the Spring Boot JAR, systemd service model, and PostgreSQL engine on a VM meets the migration goals; Kubernetes, Cloud Foundry, or PostgreSQL Flex would instead be Replatform. Derive the delivery sequence from that decision: Landing Zone, Terraform infrastructure, Ansible configuration, separate PostgreSQL migration, and the rehearsed runbook.

Design and mobilizeDesignRehost In 2 trails
R-strategy migration method Decision flow from discovery to production with the seven R-strategies: Relocate, Rehost, Replatform, Repurchase, Refactor, Retain, and Retire. R-strategy migration methodFrom discovery and path selection through the seven R-strategies to validation, transition, and production.DiscoveryDiscoveryAssess / prioritizeAssess / prioritizeDetermine migration pathDetermine migration pathValidationValidationTransitionTransitionProductionProductionRelocateRelocate(move VM)Define Landing ZoneDefine Landing ZoneUse migration toolsUse migration toolsAUTOMATEMANUALInstallInstallConfigConfigDeployDeployValidation & handoverRehostingRehosting(move application)Define Landing ZoneDefine Landing ZoneUse migration toolsUse migration toolsAUTOMATEMANUALInstallInstallConfigConfigDeployDeployReplatformingReplatforming(lift and reshape)Define Landing ZoneDefine Landing ZoneMap Target PlatformMap Target PlatformAdapt Platform StackAdapt Platform StackRepurchasingRepurchasing(replace, drop and shop)Purchase COTS/SaaS and licensingPurchase COTS/SaaS and licensingMigrate business processMigrate business processRefactoringRefactoring(re-architecting applications)Redesign application/ infrastructure architectureRedesign application/ infrastructure architectureApp code developmentApp code developmentFull ALM/SDLCFull ALM/SDLCIntegrationIntegrationRetain/moveRetain/movekeep for now or move laterRetire/decommissionRetire/decommissionLanding zone foundationLanding zone foundationShared platform base for all paths
R-strategy method with Rehost as the application-level lift-and-shift path

Rehost (lift-and-shift) migrates workloads with minimal application change. It is primarily a run strategy to reduce transition risk and accelerate migration throughput.

In practical terms, Rehost is application-wave oriented: each workload gets a defined target runtime mapping, cutover path, and runbook package for repeatable factory delivery.

STEP

Automate with Terraform and Ansible

Separate infrastructure lifecycle from target configuration: Terraform or OpenTofu creates and reconciles STACKIT resources, while Ansible configures the reachable operating system, middleware, application, and validation controls.

Design and mobilizeLanding zonesAutomation (IaC) In 3 trails

Terraform/OpenTofu and Ansible delivery flow

Section titled “Terraform/OpenTofu and Ansible delivery flow”

Terraform or OpenTofu and Ansible solve different parts of one delivery workflow. Keep the boundary explicit so infrastructure changes remain reviewable and host configuration remains repeatable.

Terraform / OpenTofu

Own the infrastructure lifecycle: projects, networks, security controls, compute, storage, managed services, and the outputs required by configuration management.

Ansible

Own configuration inside the reachable target: operating-system packages, middleware, application artifacts, service units, and workload-level validation.

  1. Version infrastructure inputs, configuration, and application artifact references in Git.
  2. Validate and review the Terraform/OpenTofu plan, including replacement and security effects.
  3. Apply the approved plan and expose only the target inventory and outputs required by Ansible.
  4. Run Ansible idempotently to configure the operating system, middleware, workload, and telemetry.
  5. Validate infrastructure state, service health, and operational controls, then retain the evidence.
  6. Promote the same versioned workflow through environments instead of repeating manual setup.

Do not use provisioners or ad hoc scripts to blur ownership between both layers. Triggering Ansible from Terraform can be a practical bridge, but each tool must remain independently understandable, testable, and rerunnable.

OPS

Target Architecture

InternetApplication ProjectPublic IPUbuntu VMObservabilityBackup ArchiveSpring Boot JAR + systemdSelf-managed PostgreSQLNode exporter restricted HTTP/SSHlocalhost SQLrestricted scrapeboot-volume backup
AUTO

Database Migration

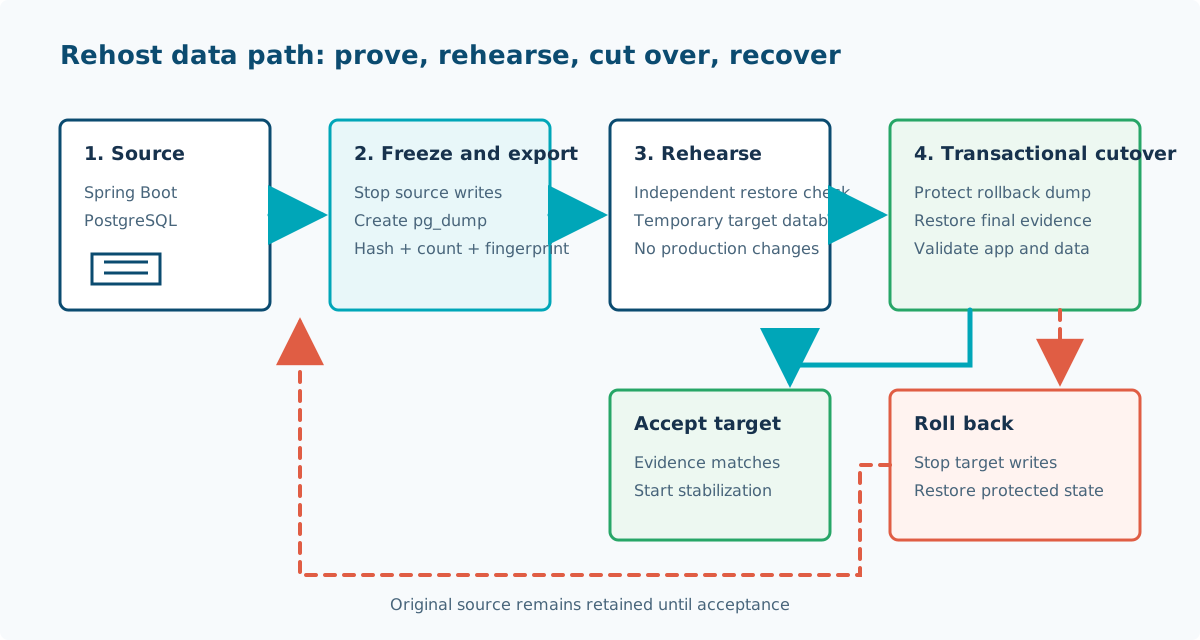
After the infrastructure and runtime path is defined, separate application preparation from PostgreSQL export, transfer, restore, and integrity validation. Define the write freeze, final dump, rollback deadline, and source retention before execution.
Design and mobilizeDesignRehost In 2 trails
Controlled PostgreSQL Rehost path from source freeze and evidence through rehearsal, transactional cutover, acceptance, or rollback

In Rehost scenarios, the data migration path depends on whether the workload is stateless or stateful:

  • Stateless workloads: Focus on application deployment and configuration.
  • Stateful workloads: Require a coordinated data movement strategy alongside the application migration.

For stateful migration waves, split the path into two streams:

  1. Infrastructure and application stream: Provision the target environment, deploy the application, and prepare the target data store.
  2. Data stream: Export source data, transfer to the target, restore, and validate.
  1. Export data from the source system using platform-native or tool-specific methods.
  2. Transfer data to the target environment or intermediate staging area.
  3. Configure the target environment to ingest the migrated data.
  4. Run the restoration process and verify data integrity.
  5. Validate application connectivity and functional behavior before final cutover.
BASE

Landing Zone

Establish the governed cloud foundation before the Rehost target depends on it. Use the six core components as the readiness frame: every control needs an owner, an approved implementation, and evidence before Terraform provisions the Spring Boot target.

Design and mobilizeLanding zonesOverview In 6 trails
Landing zone core components Six building blocks of a secure landing zone. Landing zone core componentsThe six building blocks of a secure platform foundation on STACKIT.Account GovernanceAccount GovernanceHow do I structure my projects?Identity & Access ManagementIdentity & Access ManagementWho can do what on the platform?Security & ComplianceSecurity & ComplianceHow do I monitor and protect?Network ArchitectureNetwork ArchitectureHow are components securely connected?Cost Management and ControlCost Management and ControlHow do I keep spending in control?Automation (IaC)Automation (IaC)How is everything delivered and managed?
Six core components of a secure STACKIT landing zone: governance, identity, security, network, cost control, and automation

A landing zone is the structured cloud foundation that defines how your organization operates on STACKIT from day 1. It combines governance, identity, security, network design, cost controls, and automation into one coherent baseline.

Without this foundation, migration waves typically stall due to missing approvals, inconsistent controls, and repeated platform decisions.

Accelerate the Foundation as Code

Use the STACKIT Landing Zone Accelerator to create reusable organization folders, platform projects, connectivity, management services, and the workload-ready Application Landing Zone before the Rehost automation deploys its VM.

Keep the boundary explicit: the Accelerator provides the governed environment; the application team deploys Spring Boot, PostgreSQL, telemetry, and backup into the approved Application Landing Zone.
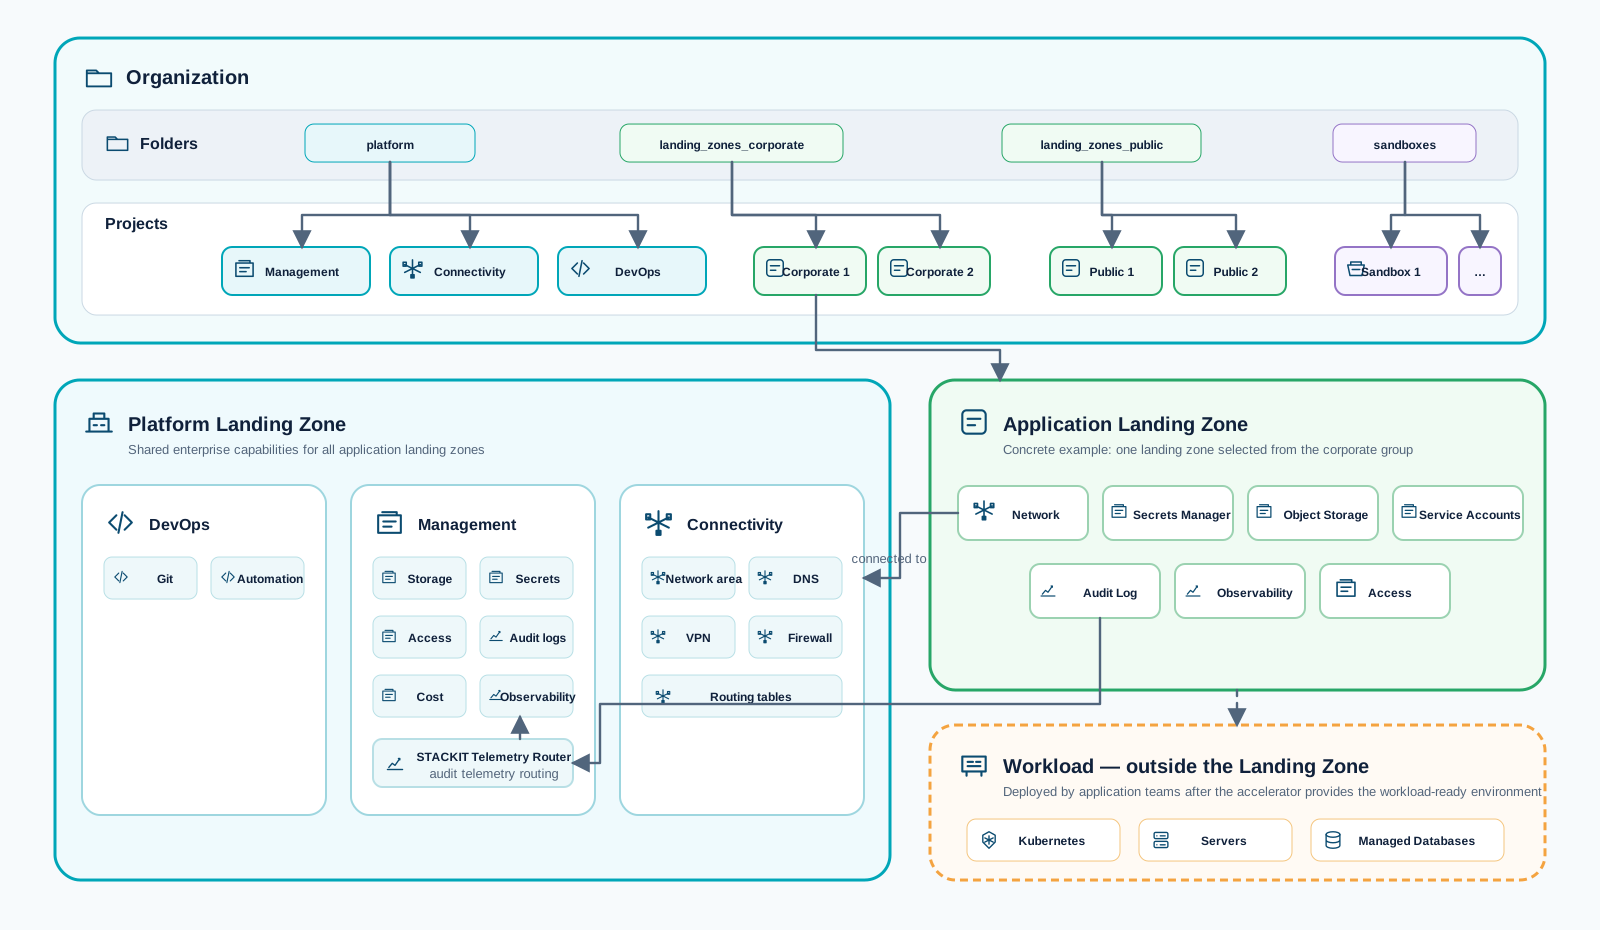
Landing Zone Accelerator architecture separating platform, application landing zone, and workload responsibilities
LIVE

Migration Framework

Enter execution only with approved design decisions, a ready Application Landing Zone, an assigned wave, and a factory-ready runbook. Execute readiness, migration, cutover, validation, stabilization, and handover as one controlled flow.

MigrateMigrateOverview In 4 trails
  1. Confirm wave scope, cutover window, rollback criteria, and runbook ownership.
  2. Freeze wave baseline (application version, dependencies, data scope, and interface contracts).
  3. Run pre-migration technical readiness checks in source and target environments.
  4. Run migration runbook steps per workload archetype and R-strategy path.
  5. Perform cutover and route traffic to the STACKIT target according to the wave plan.
  6. Validate technical, functional, and operational acceptance criteria.
  7. Stabilize incidents and known defects in short feedback loops.
  8. Hand over stabilized workloads to Optimize and Operate.
SAFE

Migration Decision Gates

  • Prepare: Approve the target design, access paths, source evidence and recovery responsibilities.
  • Provision: Review and apply the infrastructure plan, then verify the VM runtime independently.
  • Rehearse: Restore into an isolated database and verify integrity without changing the application database.
  • Cut over: Freeze source writes, approve the final dump and allow only the intended orchestration change.
  • Accept or recover: Require data, runtime and no-op evidence; invoke the agreed rollback before its deadline when acceptance fails.
  • Handover: Transfer monitoring, backup ownership, evidence and source-retention decisions before optimization.
GOAL

Optimization

Return from the concrete migration example to the Migration Framework. Start optimization only after stable cutover, use representative production telemetry, implement one controlled change at a time, and validate its effect on reliability, performance, and cost.

MigrateOptimizeOverview In 7 trails

Optimize starts when workloads run on STACKIT and real operating data is available. The module converts post-cutover observations into measurable improvements for performance, stability, and cost efficiency.

Optimize is not a one-time task. It is an iterative cycle that can overlap with early stabilization and post-cutover care.

Many right-sizing and tuning decisions are only reliable under real load patterns. After cutover, teams can use production telemetry to separate assumptions from actual behavior.

  1. Collect runtime evidence: utilization, latency, error rates, throughput, and cost drivers.
  2. Identify bottlenecks and waste patterns at workload, platform, and data layers.
  3. Prioritize actions by business impact, risk reduction, and FinOps effect.
  4. Implement tuning changes in controlled increments.
  5. Validate outcomes against SLO, reliability, and cost targets.
  6. Feed lessons learned into future migration waves and operating standards.
  • Rightsizing: Align compute, storage, and network capacity with actual demand profiles.
  • Performance tuning: Improve latency and throughput through configuration, scaling, and architecture adjustments.
  • Reliability hardening: Reduce incident frequency through better resilience, observability, and failure handling.
  • FinOps controls: Improve cost transparency, remove waste, and optimize run-rate efficiency.
STACKIT LogoSTACKIT Logo
Optimize Rehost Spring Boot with Observability and VM Rightsizing STACKIT · Runbook Open asset ↗

Use the dashboard to review infrastructure saturation, application health, request behavior, and alert history together before changing VM capacity.
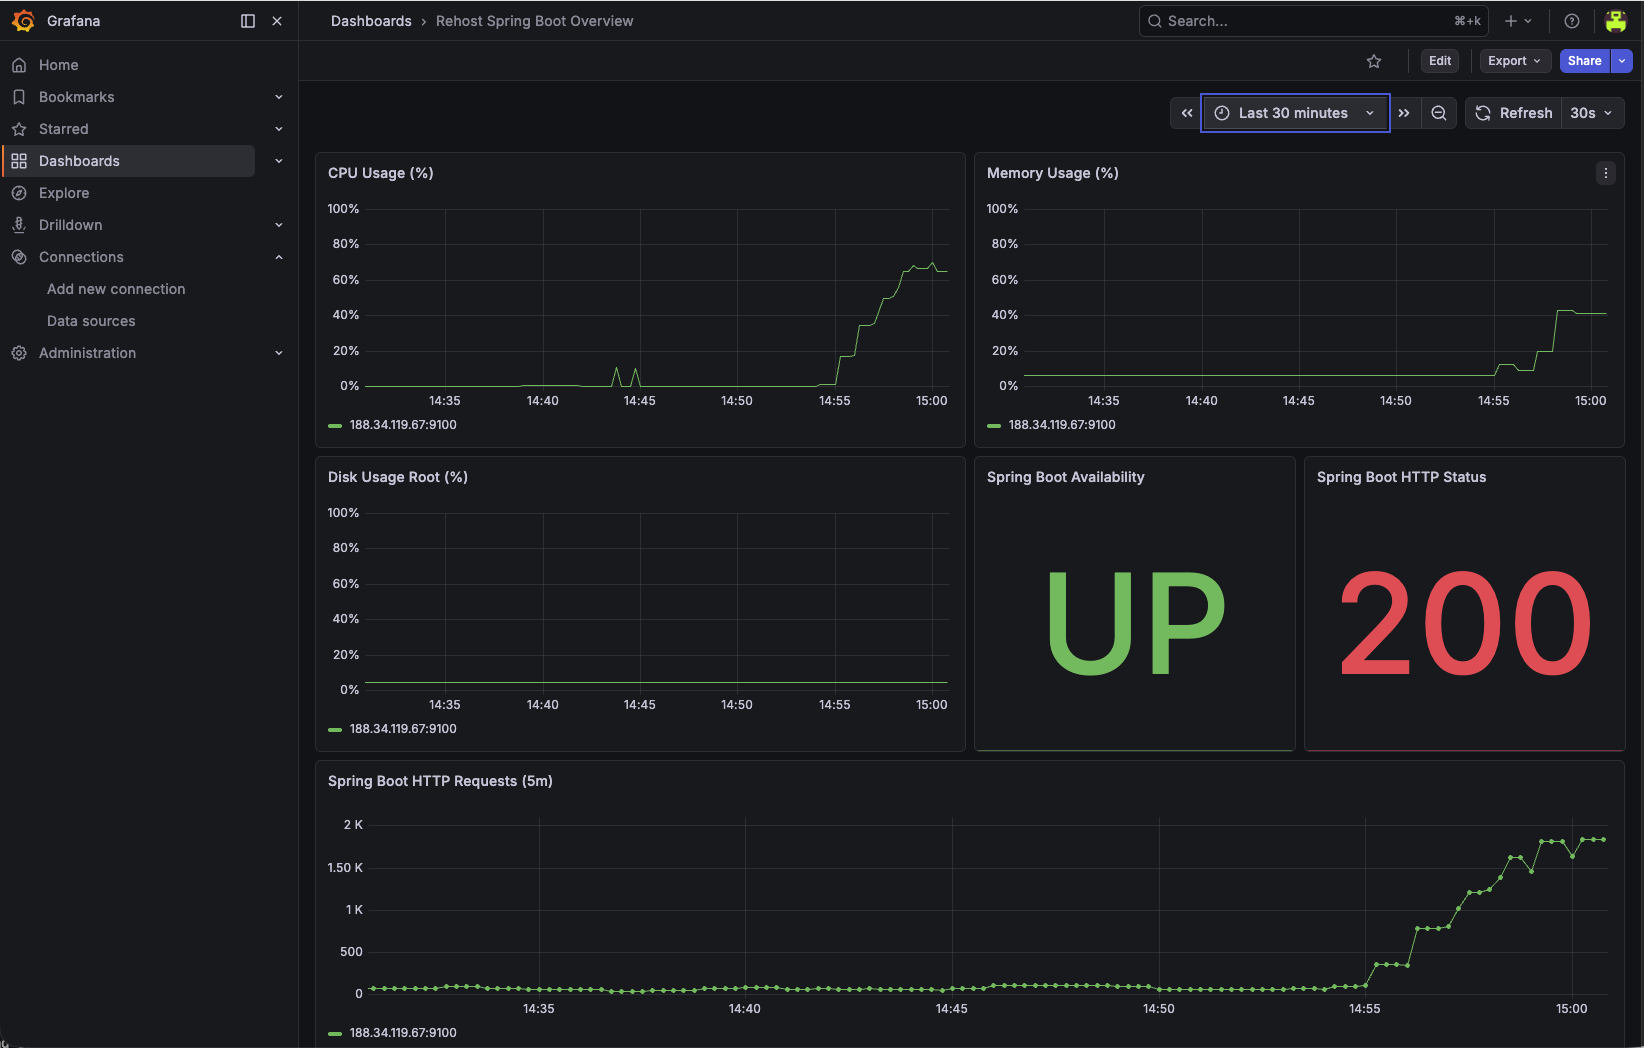
Grafana dashboard for Rehost Spring Boot observability and VM rightsizing decisions
Trail historyActive 2 of the last 12 weeksLWUpdatedNo updates · 1 bar = 1 week i
Maintainer
LWLukas WeberrußHead of STACKIT Cloud Migration Framework · STACKITOwnerActive 12 of the last 12 weeks · 58 updatesSTACKITwww.linkedin.com/in/lukas-weberruß-a360b081Contributed in STACKIT
Show full history (1 more)